ilert now supports a native Bleemeo integration


Bleemeo monitoring now connects natively to ilert, linking threshold detection to on-call management and alerting. DevOps, SRE, and IT operations teams get a direct path from a breached threshold to the phone of the engineer who can fix it, and back to a clean slate once the problem is gone.
What is Bleemeo?
Bleemeo is a cloud monitoring platform that covers servers, Docker containers, Kubernetes clusters, AWS and Azure resources, VMware environments, and SNMP network devices, all from one SaaS console. It also handles uptime checks, application performance, and logs, so teams can watch their infrastructure and the services running on it in one place.
Data collection runs through Glouton, Bleemeo's open-source agent. Alerting rules are threshold-based with separate warning and critical levels, and teams that want finer control can express conditions in PromQL.
Why connect Bleemeo to ilert?
Bleemeo is good at detecting that something is wrong. What happens next, who gets woken up, and what follows if they don't answer, is where ilert takes over.
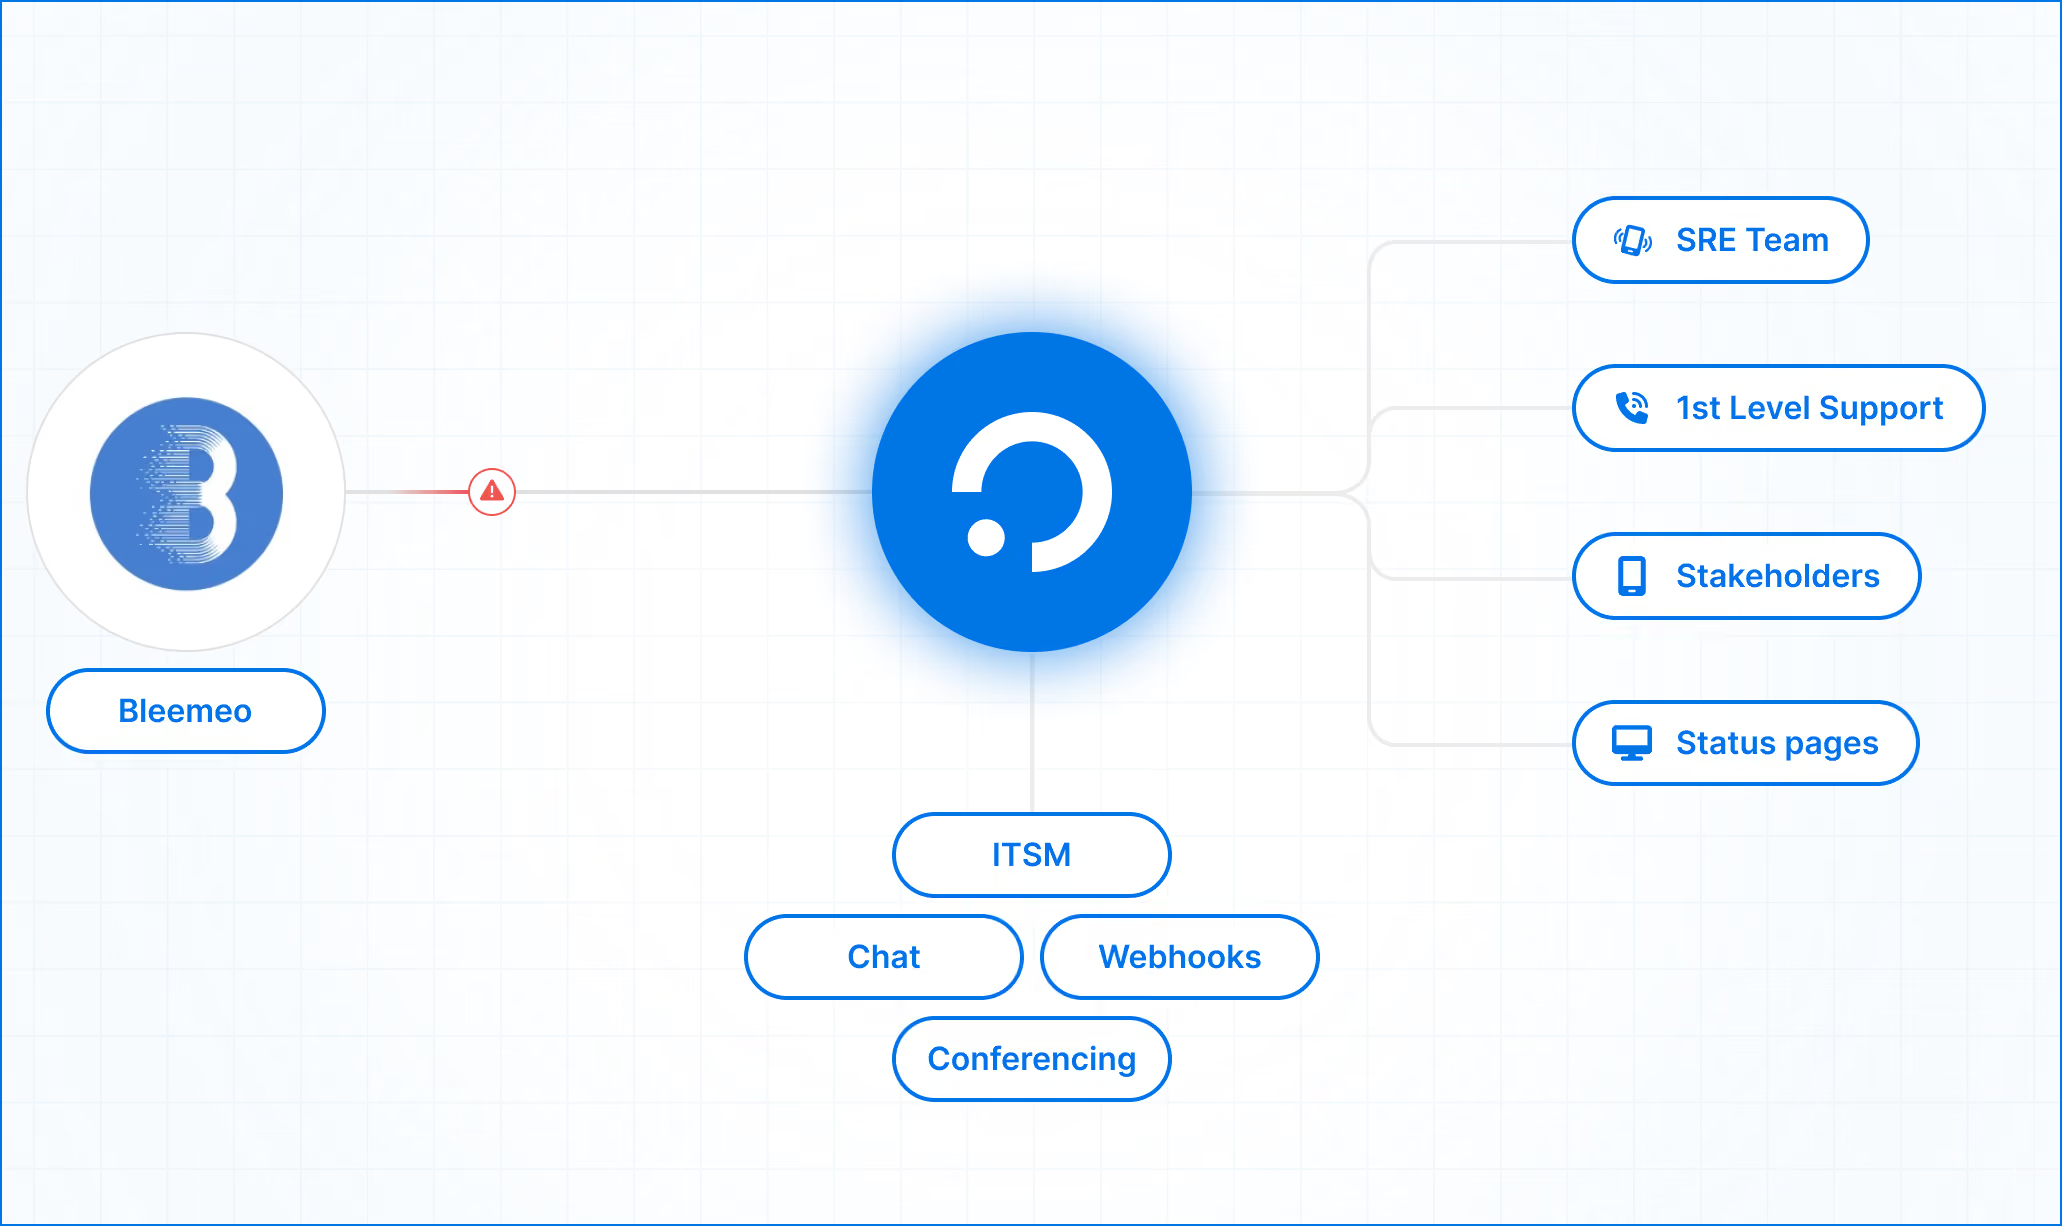
Once the integration is live, Bleemeo sends its notifications to a dedicated source in ilert. From there, ilert applies your escalation policy and on-call schedule and reaches the responder on duty via push, SMS, voice call, or chat, escalating automatically if nobody acknowledges.
Paging is where ilert starts, not where it ends. The same alert can become a declared incident with its own channel and incident commander, a status page update for customers, and a postmortem once it's closed.
Two details matter day to day. First, resolution is automatic: when the issue clears in Bleemeo, ilert closes the corresponding alert, so what's open reflects the real state of your systems instead of a backlog someone has to tidy up. Second, grouping happens per monitored metric, or per agent for agent-level events. Repeated notifications about the same problem update the existing entry rather than piling up new ones, so a struggling host wakes you once, not fifty times.
Two European platforms, one alerting chain
Bleemeo is a French company, founded in Toulouse in 2015, with metrics and logs stored in the EU. ilert is a German company in Cologne, hosted in EU data centres and ISO 27001 certified. For teams working under GDPR, NIS2, or DORA scrutiny, that means a monitoring-to-paging chain where both counterparties contract under European law, one fewer subprocessor conversation in the security review.
Set up the integration in three steps
1. In ilert:
- Go to Alert sources and create a new one
- Search for Bleemeo and select it
- Give it a name, assign teams, choose an escalation policy, and set your grouping preference
- Finish setup and copy the integration key
2. In Bleemeo:
- Open Administration → Integrations and click Add Integration
- Select ilert, paste the key, and add a descriptive name such as "Production On-Call"
3. Route your alerts:
- Go to Notifications, create a new rule or edit an existing one
- In the Targets step, select your ilert integration
Because ilert ships a purpose-built source for Bleemeo, there is no field mapping to configure. Alerts flow inbound, from Bleemeo into ilert, and setup takes a few minutes end to end.
For the full step-by-step guide, visit docs.ilert.com. If you run into any issues, our support team is ready to help at support@ilert.com.